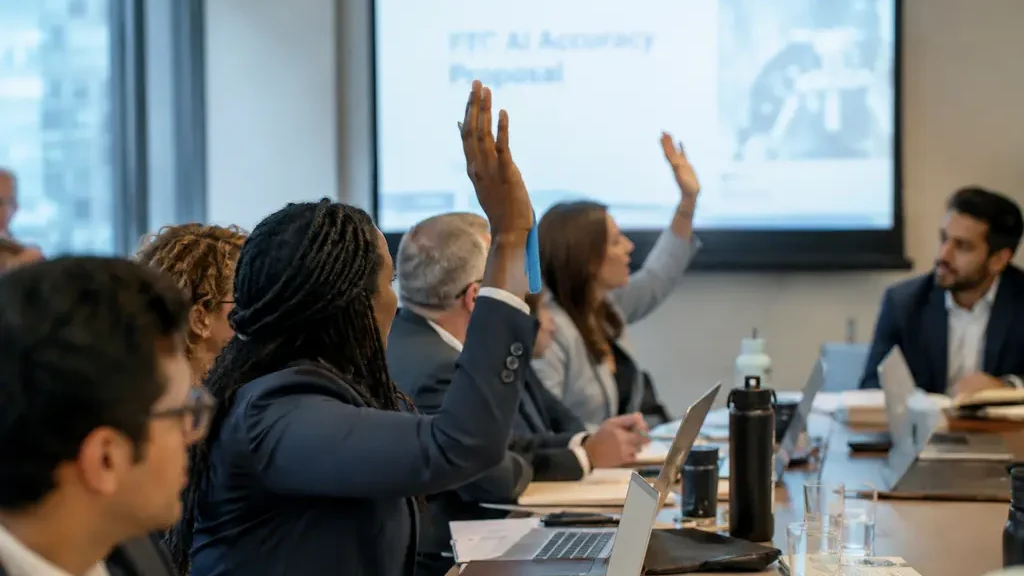
The FTC AI accuracy comment period is no longer an upcoming event. The public window opened on June 30, 2026, and closed on July 31, 2026, so industry attention should now shift from drafting comments to reading the proposal as an enforcement signal and reviewing internal AI governance evidence.
The Federal Trade Commission published its proposed policy statement on suppression of accuracy in artificial intelligence systems on July 1, 2026, under Docket Number FTC-2026-0859, according to the FTC proposal. The proposal was later published in the Federal Register on July 7, 2026, as Document Number 2026-13628, Vol. 91 FR 41638, according to the Federal Register notice.
What The FTC AI Accuracy Proposal Said
FTC AI Accuracy And Section 5
The proposal framed output steering through the FTC’s existing Section 5 authority, which prohibits unfair or deceptive acts or practices. That matters because the document was not written as a new technical standard for model quality. It instead described circumstances in which claims about AI systems, or undisclosed design choices affecting outputs, could create deception risk.
The proposed statement focused on situations where an AI system is designed or constrained in ways that depart from what consumers reasonably expect about accuracy. The core issue is not that every model error becomes a legal problem. The proposal distinguished deliberate suppression or distortion of accuracy from unintentional errors often described as hallucinations. Based on the research record, unintentional errors alone were not described as a Section 5 violation absent a misrepresentation about their frequency or nature.
Output Steering Is Not Treated As Ordinary Error
For product, policy, and engineering teams, the most practical distinction is between accidental inaccuracy and planned output steering. If a system is intentionally constrained to prioritize goals other than accuracy, the FTC’s proposal indicates that users may need clear information about that design choice. The research record identifies examples such as fairness, safety, ideology, or other objectives that may affect what the system returns.
This is especially relevant for telecom and enterprise software teams that embed generative AI into customer support, network operations, compliance workflows, content tools, or internal knowledge assistants. A customer-facing assistant that suppresses or reshapes truthful information for a non-obvious reason creates a different risk profile than a tool that occasionally produces an unintended factual error. The first issue raises questions about design intent, disclosures, and user expectations; the second raises questions about validation, monitoring, and claim discipline.
Evidence Companies Should Preserve After The Comment Window
Disclosure Records
Because the comment period has closed, companies cannot treat this as a future filing calendar item. The work now is evidence review. The proposed statement described truthful, non-misleading, clear, and conspicuous disclosures as a way firms could reduce Section 5 risk when systems are designed or constrained to prioritize objectives that differ from what users might expect.
That standard puts pressure on more than legal copy. Teams should be able to show where disclosures appear, how they are presented, and whether they remain visible at the point of use. Fine print buried in a long policy document may be difficult to defend if the product experience presents the system as neutral, objective, or fully accurate. For related coverage on records and deployment controls, see this analysis of AI accuracy compliance signals.
Architecture Records
The technical file matters as much as the public language. Model cards, system prompts, retrieval rules, safety layers, ranking logic, post-processing filters, human review policies, and release notes may all help explain whether an output was shaped for accuracy, risk reduction, brand policy, legal compliance, or another goal. The proposal does not require a specific architecture, but it does place weight on whether the company’s conduct and claims align with the system’s real behavior.
For telecom operators, AI vendors, and managed service providers, this means product documentation should connect model behavior to operational controls. If a network support assistant ranks troubleshooting guidance based on internal policy, risk rules, or permitted answer categories, records should show that design choice. For teams connecting AI governance with infrastructure and compute operations, related technical context is available through an article on hardware server coverage.
State Law Friction And Operational Risk
Preemption Claims Remain Policy Signals
The proposal also addressed potential conflict with state AI laws. The research record notes that it discussed state laws requiring alteration of truthful AI outputs and suggested that such laws may be impliedly preempted when they conflict with Section 5 obligations. The Colorado AI Act was identified in the research as one example in this debate.
Industry should be careful with this point. The statement was proposed guidance, not a final rule, and it did not by itself resolve every state-federal conflict. It did, however, give companies a reason to map where state compliance obligations could require changes to model outputs, user disclosures, or automated decision processes. The cautious reading is that compliance teams should document the conflict analysis rather than assume either state law or federal enforcement theory will automatically control every scenario.
Marketing Claims Need Technical Backing
The FTC AI accuracy proposal also affects product messaging. Claims that an AI system is objective, unbiased, neutral, fully accurate, or truth-preserving should be reviewed against system design. If the system has explicit constraints that change outputs for non-accuracy goals, the claim may need qualification. If the system is not tested for a stated level of performance, the claim should not imply that such testing exists.
This is a familiar issue for telecom professionals who already work with reliability claims, coverage representations, and service-level commitments. The same discipline applies here: do not let promotional language outrun engineering evidence. A defensible statement should be traceable to test records, configuration controls, monitoring results, and known limitations.
Operational Checklist For AI Product Teams
What To Review After July 31
The comment deadline has passed, but the policy file remains useful for internal readiness. As of October 29, 2026, the research record states that no final policy had been issued. That means companies should avoid treating the proposal as binding law while still taking it seriously as a signal of how the agency was considering Section 5 enforcement.
- Review public claims about accuracy, neutrality, objectivity, and output reliability.
- Identify where model outputs are intentionally constrained or steered.
- Check whether disclosures are clear, conspicuous, and presented near the relevant user action.
- Preserve records showing why non-accuracy objectives were implemented.
- Map state AI obligations that may affect truthful outputs or required disclosures.
This review should be practical rather than theatrical. A small deployment with limited external use may need a lighter record than a high-volume customer-facing system. The key is proportionality: the more a system affects customers, compliance decisions, operational availability, or regulated communications, the stronger the evidence trail should be.
FTC AI Accuracy Comment Period Lessons For Telecom Teams
Why The Closed Event Still Matters
The closed FTC AI accuracy comment period matters because it moved a specific issue into the policy record: whether companies can shape AI outputs while still presenting the system as accurate in the way users reasonably expect. That question is not limited to consumer chatbots. It can reach support tools, sales assistants, field-service copilots, compliance review systems, and internal decision support used by communications providers.
The safest operational response is not to stop using AI systems. It is to align claims, disclosures, architecture records, and monitoring. If a model is designed to suppress certain outputs, favor certain answer categories, or prioritize policy goals over factual completeness, that choice should be visible to the teams responsible for product approval, risk review, and customer communications.
The proposal remains nonbinding as of October 29, 2026, and no final policy has been issued according to the research record. Even so, the closed comment period left a clear compliance signal: AI accuracy claims should be narrower, better evidenced, and closer to the way systems actually behave in production.